Cloud Planning
Part of Cloud networking
Connecting an office network to cloud workloads
An office-to-cloud connection should be designed around the applications staff need, not a blanket path to every cloud address.
Start with the applications staff need to reach. Record the users, workload endpoints, data sensitivity and required protocols, then decide whether each application needs private network connectivity.
Choose a site-to-cloud VPN, a dedicated cloud interconnect or an SD-WAN connection. A VPN uses the public internet to reach a cloud gateway; Google Cloud offers cloud VPN and interconnect options, while named dedicated services include AWS Direct Connect, Azure ExpressRoute and Google Cloud Dedicated Interconnect.
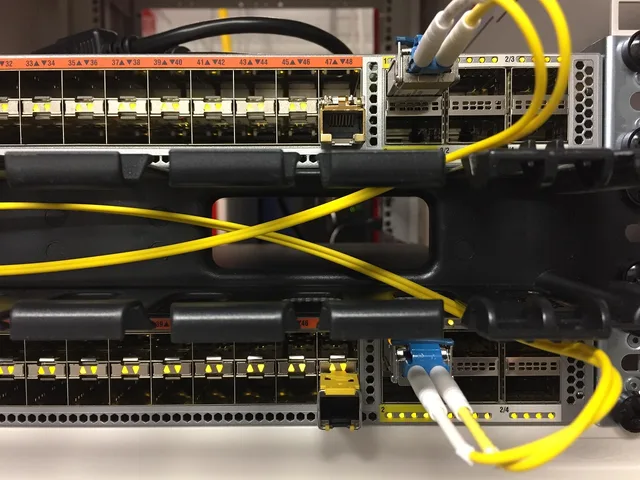
For a dedicated connection, the path can use a dedicated cloud-provider port at a carrier-neutral data centre. If your network is in the same facility, a cross-connect can link it to the port; otherwise, network service provider infrastructure can provide the path. Arelion describes NSP interconnects, with Ethernet or wavelengths as connection options.
Arrange the office-side and cloud-side connection with the relevant providers. For a logical cloud on-ramp, VLANs and BGP can establish the connection; Google Cloud Network Connectivity Center can synchronise router-appliance routes dynamically via BGP to Cloud Router and VPCs.
Configure routes in both directions between the office address ranges and the cloud workloads. Check that address ranges do not conflict and that firewall rules allow only the required traffic.
For private endpoints, make sure the office resolver returns the intended private address for the service. Azure identifies an unlinked private DNS zone, a missing or stale A record, or custom DNS or conditional forwarders not forwarding privatelink.* queries to Azure DNS (168.63.129.16) as common causes of resolution failures.
Test from a representative office device: use nslookup or dig to check name resolution, test the destination port, then perform an application action with the intended user identity. Record which step fails; a tunnel showing “connected” does not prove the application works.
Before rollout, assign owners for routing, DNS and application access, and agree on a rollback.
Cloud Connectivity Options: Comparison
- Site-to-Cloud VPN
- Uses public internet; cost-effective but less secure; suitable for low-latency needs
- Dedicated Interconnect (e.g., Direct Connect, ExpressRoute)
- Private, high-performance path via carrier-neutral data centre; ideal for sensitive workloads
- SD-WAN
- Intelligent traffic steering across multiple links; supports hybrid cloud and dynamic optimisation